MCViewPoint

Opinion from a Libertarian ViewPoint

Archive for the ‘Uncategorized’ Category

The Dignity of Risk – EPautos – Libertarian Car Talk

Posted by M. C. on February 4, 2020

I think a free man has the right to assume the dignity of risk; to weigh for himself the pros and cons – and to accept whatever consequences (good and bad) flow from his choices. To not be controlled – and to control no one else.

This is freedom. This is liberty.

https://www.ericpetersautos.com/2020/02/03/the-dignity-of-risk/

By eric

A reader took issue with me over my recent column about papier mache cars. He argued that:

“Cars and bumpers and hoods can be replaced. You cannot. Sure you can be repaired but given the large number of traffic fatalities, this can’t be ignored. Future generations will wonder at how we as a society/planet tolerated such huge dangers. Thousands dead each year.”

I am not suggesting people drive cars that are less – or more – crashworthy. I merely suggest that they be free to choose for themselves.

Obesity and diabetes “kill” thousands, too. Should the government be empowered to fine people who eat too much candy? Or to threaten everyone with fines who doesn’t exercise regularly? Some people (e.g., the loathsome Michael Bloomberg) think so! And they think so because it empowers them to control others. To control everyone.

I think differently.

I think a free man has the right to assume the dignity of risk; to weigh for himself the pros and cons – and to accept whatever consequences (good and bad) flow from his choices. To not be controlled – and to control no one else.

This is freedom. This is liberty.

No one else is harmed thereby – unless the idea that someone else’s poor choices impose an obligation enforceable at gunpoint upon others who had nothing to do with those choices is accepted as morally legitimate.

I can think of almost no doctrine more vicious or evil. To be held responsible for harms caused by others; to be restricted – and punished – without having caused any harm to anyone else.

Whom did I harm by driving a ’74 Beetle for several years after college? The car was incredibly flimsy in terms of its ability to protect me in a crash. But I never did crash the VW  – and so its crashworthiness was irrelevant. A hypothetical benefit I chose to forgo in return for the actual and tangible benefit of a very light (just 1,600 pounds) and very simple and very inexpensive car. Those attributes mattered to me, as a young man with not much money, much more than the car’s hypothetical “crashworthiness.”

Nowadays, young people without much money are denied that choice.

What gives anyone the right to tell another adult that they may not drive a certain type of car – or that a car must meet their standards?

Are we children? Property?

Are you?

The answer has to be one – or the other – because a free man isn’t either of those things and yet he is forced to buy a “crashworthy” car, because some people believe they are either the parents of other adults or that they have a kind of ownership interest in other adults and that their interest in protecting their property justifies such things.

If a man is free then he has the absolute right to weigh and assume risk – and accept the consequences as well as reap any benefits.

It does not matter, morally, whether other people are not comfortable with the risk being assumed. Or even if the risk assumed results in harm to the person who chose to assume it.

It is none of their business.

The usual reply is that it may become their business – either in the form of direct or incidental harm to them.

But this conjecture – not fact. And to arrogate the power to lord it over others based on conjecture about what may happen – before anything happens – is to arrogate power without limit, because anything can be conjectured – and anything may happen.

What actually happens is another matter.

To require that it actually does happen – that harm is caused – before holding the person accountable is a necessary prerequisite of justice because it is the incarnation of injustice to make a man pay for a harm he has not caused.

Also to make others pay for the harm he has caused, if he does cause it.

This is the usual basis for justifying punishing – and controlling – people who’ve caused no harm to anyone, including themselves – but might.

The argument is that – as in my case – driving a car that is not as “crashworthy” as it could be if it were more heavily constructed, had multiple air bags – and so forth – puts society at risk of harm. That if I had an accident and had been injured, the costs of my injuries would be born by society and thus, society has the moral right to apply pre-emptive protection measures to assure the risk to myself is lower, in order to protect itself from liability.

This doctrine is even more vicious than the first (that free adults are in fact idiot children or a species of property, like cattle) because it is essential to the power of the first doctrine.

It is the method by which free men can be treated as idiot children and cattle without actually calling them those things, openly.

There is no such thing as society except in a rhetorical sense. There are only the individual men and women who, together, exist in society.

The fact that people exist in society does not give “society” rights, let alone rights superior to those of actual men and women.

You attend a dinner party; there are other people present. Your are in society with them. Attending the dinner party doesn’t give your host the right to force you to eat what is served nor you to force him to serve you.

In practice, “society” – as defined by the Bloombergs who crave to rule it – is a few of the individuals who exist within it who presume to have parental or ownership rights over other individuals within society. They claim to “represent” society. Perhaps they do speak for some of the individuals within society – but certainly not every individual. In which case, the not-represented individuals are treated as idiot children and property by the those who think they are the parents and owners.

But instead of being honest about this, they talk about the costs to society of risks taken, of choices made -whether harm is caused or not.

This is a danger that “future generations will wonder at how we as a society/planet tolerated.”


Be seeing you

Tag


Posted in Uncategorized | Tagged: , , , | Leave a Comment »

Failed Coup of a Failing Establishment – LewRockwell

Posted by M. C. on February 4, 2020

The damage they have inflicted upon our country’s institutions is serious.

U.S. intelligence agencies are being investigated by U.S. Attorney John Durham for their role in instigating an investigation of a U.S. presidential campaign. The FBI has been discredited by exposure of a conspiracy of top-level agents to spy on Trump’s campaign.

https://www.lewrockwell.com/2020/02/patrick-j-buchanan/failed-coup-of-a-failing-establishment/

By

It has been a bad few days for the establishment, really bad.

In a 51-49 vote, the Senate refused to call witnesses in the impeachment trial of Donald Trump and agreed to end the trial Wednesday, with a near-certain majority vote to acquit the president of all charges.

As weekend polls show socialist Bernie Sanders surging into the lead for the nomination in the states of Iowa, New Hampshire and California, the sense of panic among Democratic Party elites is palpable.

Former Secretary of State and Joe Biden surrogate John Kerry was overheard Sunday at a Des Moines hotel talking of the “possibility of Bernie Sanders taking down the Democratic Party — down whole.”

Tuesday, Trump takes his nationally televised victory lap in the U.S. Capitol with his State of the Union address, as triumphant Majority Leader Mitch McConnell and a humiliated Speaker Nancy Pelosi sit silently side-by-side behind him.

Democrats may declare the Trump impeachment a victory for righteousness, but the anger and outrage, the moans and groans now coming off the editorial and op-ed pages and cable TV suggest the media know otherwise.

History, we are told, will vindicate what Pelosi and the Democrats did and stain forever the Republican Party for voting to acquit.

Perhaps, but only if some future Howard Zinn is writing the history.

Reality: The impeachment of Trump was an attempted — and failed — coup that not a single Republican supported, only Democrats in the House and their Senate caucus. The impeachment of Trump was an exercise in pure partisanship and itself an abuse of power.

What was the heart of the Democrats’ case to remove Trump?

Trump failed to invite Ukrainian President Volodymyr Zelenskiy to the White House, and held up military aid to Kyiv for several months, to get Zelenskiy to hold a press conference to announce that Kyiv was looking into how Hunter Biden got on the board of a corrupt energy company at a retainer of $83,000 a month while his father was the chief international monitor of corruption in Ukraine.

The specific indictment: Trump’s suspension of military aid imperiled “our national security” by denying arms to an “ally” who was fighting the Russians over there, so we don’t have to fight them over here.

And what was the outcome of it all?

Zelenskiy got his meeting with the president. He got the military aid in September. He did not hold the press conference requested. He did not announce an investigation of the Bidens.

No harm, no foul.

How did President Obama handle Ukraine?

After Vladimir Putin annexed Crimea and intervened to protect pro-Russian secessionists in the Donbass, Obama’s White House restricted U.S. lethal military aid to Kyiv and provided blankets and meals ready to eat.

What punishment did House and Senate Democrats and anti-Trump media demand for the pause in sending weapons for Ukraine?

Capital punishment, a political death penalty.

Democrats demanded that a Republican Senate overturn the election of 2016, make Trump the first president ever impeached and removed, and then ensure that the American people could never vote for him again.

Nancy Pelosi’s House and the Democratic minority in the Senate were demanding that a Republican Senate do their dirty work and keep Trump off the ballot in 2020, lest he win a second term.

For four years, elements of the liberal establishment — in the media, “deep state” and major institutions — have sought to destroy Trump. First, they aimed to smear him and prevent his election, and then to overturn it as having been orchestrated by the Kremlin, and then to impeach and remove him, and then to block him from running again.

The damage they have inflicted upon our country’s institutions is serious.

U.S. intelligence agencies are being investigated by U.S. Attorney John Durham for their role in instigating an investigation of a U.S. presidential campaign. The FBI has been discredited by exposure of a conspiracy of top-level agents to spy on Trump’s campaign.

The media, by endlessly echoing unproven claims that Trump was a stooge of the Kremlin, discredited themselves to a degree unknown since the “Yellow Press” prostituted itself to get us into war with Spain. Media claims to be unbiased pursuers of truth have suffered, not only from Trump’s attacks, but from their own biased and bigoted coverage and commentary.

The NSC and State Department have been exposed as employing individuals with an exaggerated view of their role in the origination and the execution of foreign policy. Disloyalty and animosity toward the chief executive appear to permeate the upper echelons of the “deep state.”

Not in our lifetime have the institutions of government and the establishment been held in lower regard.

Almost all now concede we have become an us vs. them nation.

How we accomplish great things again, giving our seemingly unbridgeable differences, remains a mystery.

Be seeing you

212002_0


Posted in Uncategorized | Tagged: , , , | Leave a Comment »

Putin in Israel | The Nation

Posted by M. C. on February 4, 2020

Looking ahead, Putin has invited Trump to join him on Red Square on May 9, Russia’s “Victory Day,” a sacred commemoration of immense importance to the Kremlin and for most of Russia’s people. Certainly, President Trump should accept, if only to honor the estimated 27 million Soviet citizens who died in World War II. But here, too, will Washington politics and media discourage him from doing so?

https://www.thenation.com/article/world/putin-in-israel/

By Stephen F. Cohen

As with its 40-year predecessor, the new US-Russian Cold War has characteristic features, including sharply conflicting historical memories. Some of them are absurdly inaccurate and politically dangerous. Consider a recent ramifying example.

On January 23, Russian President Vladimir Putin was in Israel to commemorate Holocaust Remembrance Day and the 75th anniversary of the liberation of Auschwitz by the Soviet (mostly Russian) army. Representatives of many other countries also attended the solemn events, including US Vice President Mike Pence, but according to the Times of Israel, Putin was “the most formidable and dominant presence.” The reason, widely acknowledged in Israel though scarcely in the United States today, is that the Soviet army, more than any other, saved the surviving Jews of Europe as it defeated Nazi Germany in route from Stalingrad to Berlin.

Ukrainians, most of them then Soviet citizens, played a large role in those historical events, both as Holocaust victims and as soldiers in the Soviet army. Nonetheless, at about the same time as the ceremonies in Israel were underway, the inveterate bipartisan anti-Russian lobby in Washington—notably at this moment Democratic Representative Adam Schiff and a predictable slew of other lawmakers and impeachment witnesses—were declaring Ukraine today’s front line against Russia’s “new aggression.” Among other things, this was not the peace with Russia promised, and indeed sought since his election, by Ukraine’s new president Volodymyr Zelensky.

At the very moment when peace between Ukraine and Russia is within reach, and with it the possibility of saving many lives, warmongering—an ugly but appropriate word—intensifies in Washington. On December 4, for example, in a formulation rarely heard since the early 1950s, a pro-impeachment witness, not known for any Russia, Ukraine, or related expertise, told Congress that the United States must make “sure that the Ukraine remains strong and on the front lines so they fight the Russians there and we don’t have to fight them here.” By January 22, this had become a warfare mantra in Congress, with Democratic Representative Jason Crow, an impeachment manager, also assuring members that America must “fight Russia over there so we don’t have to fight Russia here.” Whatever the merits of the impeachment process, its legacy, as I have warned from the outset, is likely to be an ever-worsening new Cold War and thus conceivably something even more dire.

Yet these fateful issues cannot be candidly discussed in Washington because they are widely regarded, as NBC’s Chuck Todd mindlessly characterized them, as “Russian talking points” and “disinformation.” By implication, and sometimes in direct accusations, anyone who does raise them is a “Kremlin apologist.”

Such continues to be the state of American discourse about this new and more perilous Cold War. Will any of the current Democratic presidential candidates change the discourse­­—or be permitted to do so by “moderators” of their debates? Or must we rely almost entirely on President Trump’s continuing, and substantially thwarted, effort to implement his campaign promise to “cooperate with Russia”?

Looking ahead, Putin has invited Trump to join him on Red Square on May 9, Russia’s “Victory Day,” a sacred commemoration of immense importance to the Kremlin and for most of Russia’s people. Certainly, President Trump should accept, if only to honor the estimated 27 million Soviet citizens who died in World War II. But here, too, will Washington politics and media discourage him from doing so?

Be seeing you


Posted in Uncategorized | Tagged: , , , , | Leave a Comment »

DOD tester’s report: F-35 is still a lemon | Ars Technica

Posted by M. C. on February 3, 2020

https://arstechnica.com/information-technology/2020/01/not-a-straight-shooter-dod-review-cites-fleet-of-faults-in-f-35-program/

The latest report on the progress of the US Defense Department’s F-35 Joint Strike Fighter is due out soon from the Office of the Secretary of Defense’s director for operational test and evaluation (DOT&E), Robert Behler.

Last year’s report was full of bad news. And based on Bloomberg Government’s Tony Capaccio’s early access to the new report, we know much of that bad news is still bad news. In fact, the only real good news is that there are no new major flaws in the $428 billion aircraft program reported by Behler’s team.

But the bad is still bad. For starters, the Air Force version of the F-35 can’t hit what it shoots its gun at.

There are a total of 13 Category 1 “must fix” issues still unresolved with the F-35 that stand between the program and final production. And even as the long list of less critical problems is addressed, new ones keep popping up. “Although the program office is working to fix deficiencies,” Behler wrote in the report viewed by Bloomberg, “new discoveries are still being made, resulting in only a minor decrease in the overall number.” And “many significant” issues remain to be addressed, he noted.

The report does not include data from the current round of combat testing, so even more problems may soon be added to the list.

ALIS doesn’t live here anymore

One of the major sources of problems with the F-35 program is the Autonomic Logistics Information System (ALIS)—the software that drives maintenance and logistics for each F-35 aircraft. ALIS is supposed to intelligently drive the flow of maintenance parts, guide support crews in scheduling maintenance, and ensure the right parts get stuck in the right places. Aircraft health and maintenance action information is sent by the ALIS software in each aircraft out to the entire distributed logistical support network.

But ALIS has had some problems—including the fact that the software was not complete when Lockheed Martin began shipping aircraft, and each group of the 490 aircraft already delivered arrived with one of six different versions of the software. All of them will require extensive software retrofits when the seventh is complete, along with the other 510 or so that are expected to have been delivered worldwide by that point.

There are still 873 specific problems in ALIS and other F-35 software (down from 917 in 2018). In fact, the DOD has announced it will replace ALIS outright, eventually.

And those have been a contributor to the F-35 fleet’s poor reliability. According to OT&E, the overall fleet of F-35s fell far short of being 80-percent “mission capable”—meaning that they could be used in at least one type of combat mission. The Navy’s F-35C fleet “suffered from a particularly poor” mission-capable rate, the OT&E team stated.

In addition to just functional software problems, the OT&E office also reported that cybersecurity issues that had been identified in previous reports on the F-35 program had still not been resolved.

Do you even shoot, bro

While the Navy and Marine Corps versions of the F-35 may have more availability problems than the relatively less-complex Air Force F-35A, they can do at least one thing better: hit what they’re shooting at.

The F-35B and F-35C have externally mounted guns, while the Air Force’s 25-millimeter cannon is mounted internally. Problems with the alignment of the gun’s mount, and the fact that the mount occasionally cracks after the gun has fired, have made the accuracy of the gun “unacceptable,” according to test officials, and have made the Air Force restrict use of the gun. While the F-35 program office has worked on improvements of the gun mount for the F-35A, these have not yet been tested.

But none of this is really slowing down acquisition of the F-35—now the most expensive DOD weapons program in history. Considering that the F-35 was originally supposed to be the “low” in the “high-low mix“—with the F-22 being the more capable aircraft—the huge cost overruns and flaws make the F-35 look increasingly like the world’s most expensive lemon.


Posted in Uncategorized | Tagged: , , , , , , | Leave a Comment »

How Government and Media Are Prepping America for a Failed 2020 Election

Posted by M. C. on February 3, 2020

Naming the culprits in advance

What has been left unsaid, however, is that a government’s solution to “chaos” is always the imposition of “order.” This means that — whatever “chaos” ultimately ensues prior to or on election day — will result in a government response that will do much more to crush freedom and undermine democracy than any act of foreign meddling has, be it real or imagined.

It wasn’t so long ago that electronic elections were our savior. The problem was the results were not as planned.

https://www.mintpressnews.com/media-israel-intelligence-2020-elections-cyber-security/264361/

By Whitney Webb Whitney Webb

As World War II drew to a close in Europe, British philosopher Bertrand Russell wrote that “neither a man nor a crowd nor a nation can be trusted to act humanely or to think sanely under the influence of a great fear.”

Though numerous examples in the post-World War II era have proven Russell’s point, perhaps one of the best examples was the U.S. public’s willingness to swallow lie after lie about Saddam Hussein’s Iraq due to the climate of fear that followed the September 11 attacks. Those lies, propagated by dubious intelligence, government officials and a compliant media, resulted in catastrophes – large and small, both abroad and at home.

Today, an analogous narrative is being crafted by many of the same players – both in media and government – yet it has avoided scrutiny, even from independent media.

Over the past several months and with a renewed zeal in just the last few weeks, anonymous intelligence officials, dubious “experts” and establishment media outlets have crafted a narrative about the coming “chaos” of the 2020 election, months before it takes place. Per that narrative, certain state actors will use specific technologies to target the “American mind” in order to undermine the coming presidential election. The narrative holds that those efforts will be so successful that the U.S. will never recover as a democracy.

Though these anonymous government sources and their stenographers have already named the countries who will be responsible and the technologies they will use, they also admit that no evidence yet exists to back up these claims, meaning they are — at best — pure speculation.

Headlines such as “Hackers Are Coming for the 2020 Election — And We’re Not Ready,” “Basically Every US National Security Leader Is Warning About Foreign Interference In The 2020 Election,” and “U.S. intel agencies: Russia and China plotting to interfere in 2020 election” have become increasingly common, despite no available evidence, as have warnings that the American public is defenseless against the old scourge of “fake news” and the new scourge of “deep fakes.” Some media reports have gone so far to say that actual foreign meddling isn’t even necessary as merely the fear of foreign meddling could be enough to upend the American political system beyond repair.

Historically, the goal of such fear-inducing narratives has been the trading of civil liberties for increased security, or rather, the appearance of increased security. Yet, when the need for security is felt due to a fear that is based on government-driven speculation and not on evidence, the goal of that narrative is not about protecting the public from a real, tangible threat but instead about the consolidation of power by the very groups responsible for crafting it — in this case, the intelligence community and other key players in the national security state.

However, what is particularly odd about this narrative surrounding imminent “chaos” and meddling in the upcoming 2020 election is the fact that, not only have the instruments of said meddling been named and described in detail, but their use in the election was recently simulated by a company with deep ties to both U.S. and Israeli intelligence. That simulation, organized and run by the Israeli-American company Cybereason, ended with scores of Americans dead, the cancellation of the 2020 election, the imposition of martial law and a spike in fear among the American populace.

Many of the technologies used to create that chaotic and horrific scenario in the Cybereason simulation are the very same technologies that U.S. federal officials and corporate media outlets have promoted as the core of the very toolkit that they claim will be used to undermine the coming election, such as deep fakes and hacks of critical infrastructure, consumer devices and even vehicles.

While the narrative in place has already laid the blame at the feet of U.S. rival states China, Russia and Iran, these very technologies are instead dominated by companies that are tied to the very same intelligence agencies as Cybereason, specifically Israeli military intelligence.

With intelligence agencies in the U.S. and Israel not only crafting the narrative about 2020 foreign meddling, but also dominating these technologies and simulating their use to upend the coming election, it becomes crucial to consider the motivations behind this narrative and if these intelligence agencies have ulterior motives in promoting and simulating such outcomes that would effectively end American democracy and hand almost total power to the national security state.


Media, intelligence foreshadow tech-powered doom for 2020

Even though the 2020 U.S. election is still months away, a plethora of media reports over the past six months (and even before then) have been raising concern after concern about how the U.S. election is still so vulnerable to foreign meddling that such meddling is essentially an inevitability.

Part of the reason for the recent pick-up in fear mongering appears to have been the release of a joint statement issued by key members of the Trump administration last November. That statement, authored by Attorney General Bill Barr, Defense Secretary Mark Esper, acting DHS Secretary Kevin McAleenan, acting Director of National Intelligence Joseph Maguire, FBI Director Christopher Wray, NSA Director Gen. Paul Nakasone, and Cybersecurity and Infrastructure Security Agency (CISA) Director Christopher Krebs, claimed that foreign interference in 2020 was imminent despite admitting that there is no evidence of interference having taken place:

Our adversaries want to undermine our democratic institutions, influence public sentiment and affect government policies. Russia, China, Iran, and other foreign malicious actors all will seek to interfere in the voting process or influence voter perceptions. Adversaries may try to accomplish their goals through a variety of means, including social media campaigns, directing disinformation operations or conducting disruptive or destructive cyber-attacks on state and local infrastructure.

While at this time we have no evidence of a compromise or disruption to election infrastructure that would enable adversaries to prevent voting, change vote counts or disrupt the ability to tally votes, we continue to vigilantly monitor any threats to U.S. elections (emphasis added).”

Despite the key caveat of there being no evidence at the time the statement was issued, media reports used the statement to claim that foreign interference in 2020 was imminent, such as in these reports from BuzzFeed, ABC News, and Newsweek.

In addition to the reports that have cast the involvement of state actors — namely Russia, Iran and China — as assured despite no evidence, other reports have made the claim that this allegedly imminent interference will inevitably be successful, largely due to claims that the tactics used will rely heavily on technology that the U.S. can’t hope to successfully counter. CSO Online, an online news outlets that provides news, analysis and research on security and risk management, recently warned that “fixing America’s voting and election infrastructure problems is a long-term proposition, one that won’t be fixed in time for the election in November” while the New York Times warned of imminent chaos and that “stealthier” malevolent foreign actors had already created the foundation for “an ugly campaign season marred by hacking and disinformation.” Wired claimed last year that U.S. election security “is still hurting at every level.”
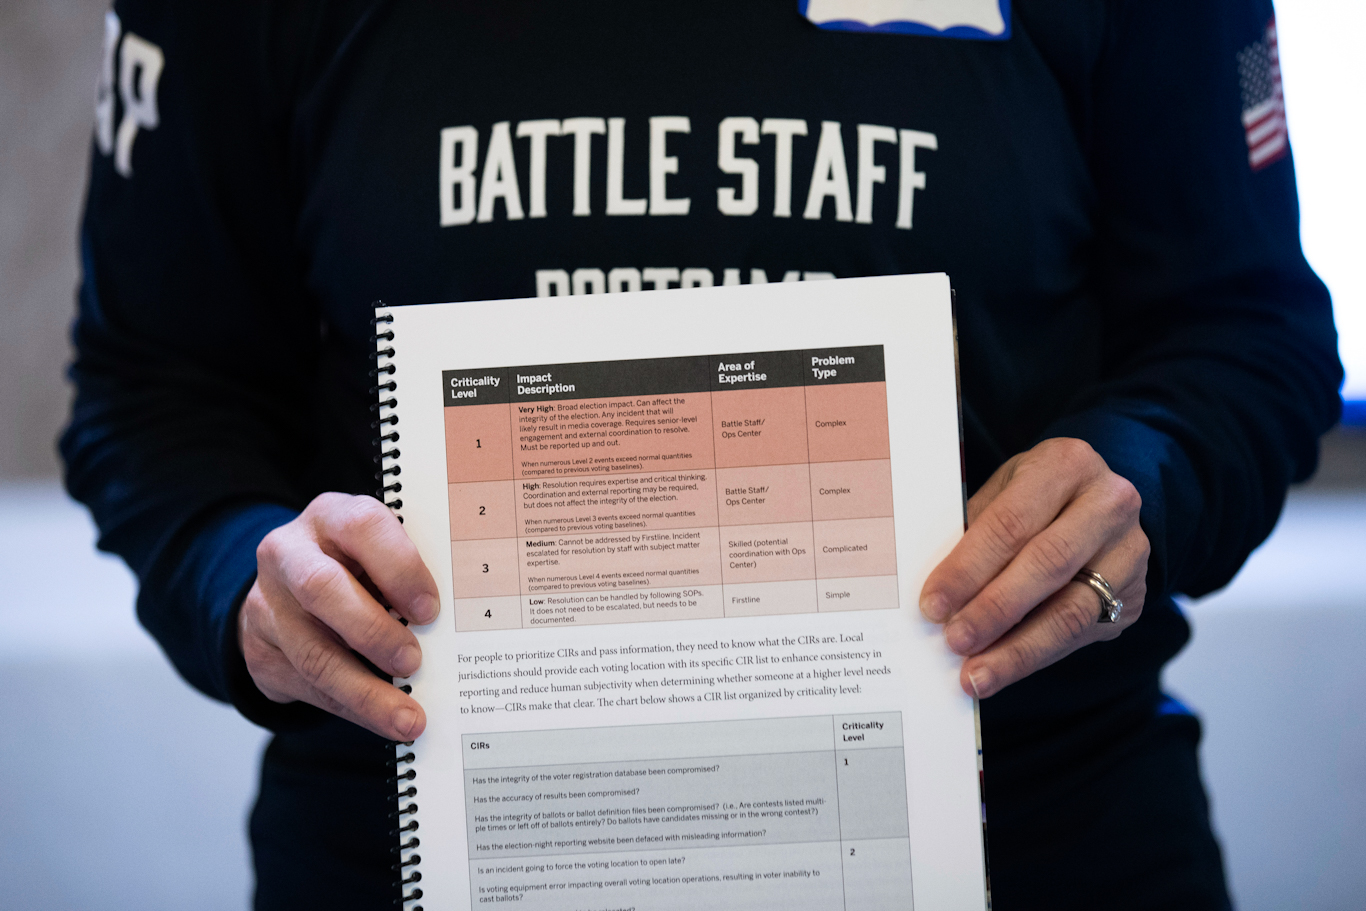
Election Security

In another example, Rolling Stone published an article earlier this month with the headline “Hackers Are Coming for the 2020 Election — And We’re Not Ready,” which claims that “the reality is that: “We’ve made progress since the last election — but we’re much less secure than we should be.” The article goes on to say that claim that the goal isn’t necessarily to hack voting machines or change results, but “to merely create the impression of an attack as a way to undermine our faith in the electoral process.”

It continues:

The target is the minds of the American people,” says Joshua Geltzer, a former counterterrorism director on the National Security Council. “In some ways, we’re less vulnerable than we were in 2016. In other ways, it’s more.” Nearly every expert agrees on this: The worst-case scenario, the one we need to prepare for, is a situation that causes Americans to question the bedrock of our democracy — free and fair elections.”

Well before this type of rhetoric made its way into the U.S. media, Israeli intelligence-linked tech firm Cybereason claiming in a release on its website that “messing with a voter’s mind” would have a bigger impact than changing vote totals, even before the 2016 election. That release, published by Cybereason prior to the last presidential election, was authored by the company’s CEO, Lior Div, who used to lead offensive hacking operations against nation-states for Israeli military intelligence.

Notably, of all of these media reports, there is a clear consensus that one of the main tactics that will soon be used to meddle in the coming U.S. election will be the use of so-called “deep fakes.” Deriving its name from a combination of “deep learning” and “fake,” deep fakes involve video and audio that has been manipulated using artificial intelligence (AI) to create media that appears to be authentic, but is not. Concern about its use in the upcoming election has spurred not only a wealth of media reports on the matter but has prompted both the U.S. military and Congress to take action to limit its potential misuse.

One thing that stands out about the media narrative regarding election meddling and deep fakes is that several news organizations have published articles that state that deep fakes will be used to undermine the 2020 election, as opposed to stating that they could be used or that they are a phenomenon worthy of attention (though some reports have taken this more measured approach).

The reason for this level of confidence may owe to statements made by prominent U.S. intelligence officials last year, including those made by Dan Coats, the former Director of National Intelligence (DNI), who claimed in the 2019 Worldwide Threat Assessment for the U.S. Intelligence Community that deep fakes and other hi-tech forms of fake media would be used to disrupt the 2020 election. Coats specifically stated:

Adversaries and strategic competitors probably will attempt to use deep fakes or similar machine-learning technologies to create convincing—but false—image, audio, and video files to augment influence campaigns directed against the United States and our allies and partners.”

Since Coats made the warning, numerous media reports have promoted the concern with little scrutiny, representing just one of the numerous times in U.S. history where narratives first authored by U.S. intelligence are subsequently promoted heavily by U.S. media, even when the claim made by intelligence officials is speculative, as it is in this case. Indeed, the narratives being promoted with respect to the 2020 election involve many of the same intelligence agencies (American and Israeli) and media outlets who promoted claims that were later proven false about “weapons of mass destruction” in Iraq prior to the 2003 invasion, among other pertinent examples.

Notably, deep fakes figured prominently and was the tool most used by malevolent hackers in Cybereason’s 2020 election simulation, which saw both video and audio-only deep fakes used to spread misinformation on national and local TV channels in order to impersonate police officers and election officials and to create fake bomb threats by posing as the terror group Daesh (ISIS). Cybereason also happens to be a partner of the organization funding the most well-known creator and producer of deep fakes in the world, an organization that — much like Cybereason itself — is openly tied to Israeli intelligence.

Aside from deep fakes, other technologies weaponized in Cybereason’s election simulation have also been the subject of several media reports, such as the hacking of Internet of Things (IoT) devices and appliances and even the hacking of vehicles that have some form of internet connectivity.  In the Cybereason simulation, IoT hacks were used to cut power to polling stations and disseminate disinformation while vehicles were hacked to conduct terror attacks against civilians waiting in line to vote, killing several and injuring hundreds.

Most media reports have claimed that these technologies will be part of the coming “explosion” in cyber warfare in 2020 and do not specifically link them to imminent election meddling. Others, however, have made the link to the election explicit.


Naming the culprits in advance

In addition to the apparent consensus on how foreign meddling will occur during the 2020 election, there is also agreement regarding which countries will be responsible. Again, this is largely based on statements made by U.S. national security officials. For instance, the joint statement issued last November by the DOJ, DOD, DHS, DNI, FBI, NSA, and CISA regarding 2020 election security, states that “Russia, China, Iran, and other foreign malicious actors all will seek to interfere in the voting process or influence voter perceptions” before adding “at this time we have no evidence.”

Similarly, the 2019 Worldwide Threat Assessment for the U.S. Intelligence Community, written by then-Director of National Intelligence Dan Coats, names these same three countries in relation to imminent 2020 election interference and states that their interference in the 2020 election is “almost certain.” The assessment adds the following about each nation:

  • Russia: “Russia’s social media efforts will continue to focus on aggravating social and racial tensions, undermining trust in authorities, and criticizing perceived anti-Russia politicians.”
  • China: “China will continue to use legal, political, and economic levers—such as the lure of Chinese markets—to shape the information environment. It is also capable of using cyber attacks against systems in the United States to censor or suppress viewpoints it deems politically sensitive.”
  • Iran: “Iran, which has used social media campaigns to target audiences in both the United States and allied nations with messages aligned with Iranian interests, will continue to use online influence operations to try to advance its interests.”

Coats’ assessment was enough to spawn numerous stories on the imminent threat that these three nations pose to the 2020 election, with headlines such as “U.S. intel agencies: Russia and China plotting to interfere in 2020 election.”

The vast majority of warnings regarding future election interference have come from U.S. intelligence officials with a dubious record of trustworthiness and a history of using the media to spread propaganda and disinformation, most famously through Operation Mockingbird. Most — if not all — of the recent and numerous articles on imminent interference rely heavily on claims made by the two aforementioned government documents, documents crafted by U.S. intelligence agencies for public consumption, as well as claims made by anonymous U.S. officials.
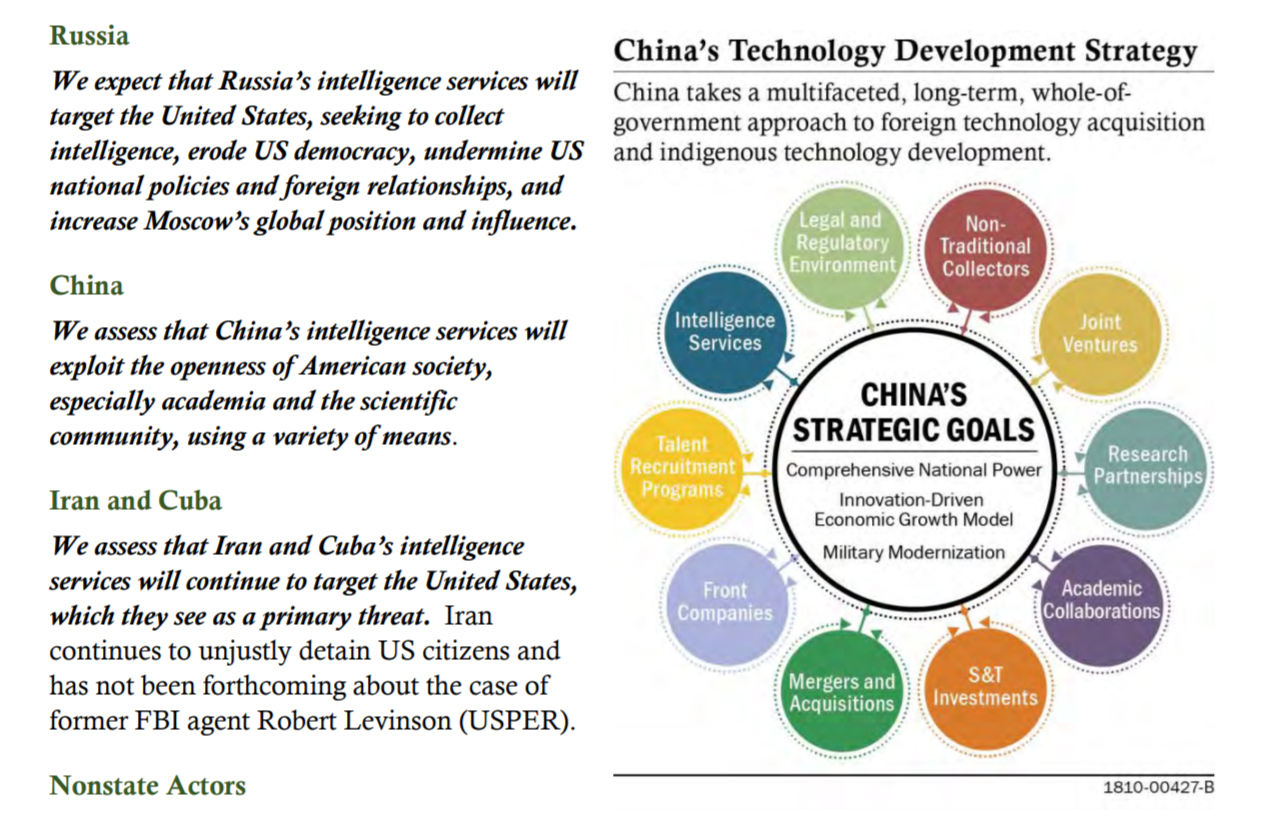
2019 National Threat Assessment

A recent New York Times article, for example, titled “Chaos Is the Point’: Russian Hackers and Trolls Grow Stealthier in 2020,” is based almost entirely on “interviews with dozens of officials and experts,” though the only government official named in the article is Shelby Pierson, the intelligence community’s election threats executive. The most quoted experts named in the article are Ben Nimmo, formerly of the hawkish, NATO-funded Atlantic Council and now with Graphika, and Laura Rosenberger, director of the neoconservative-created Alliance for Securing Democracy. The article nonetheless cites “American officials” and “current and former officials” several times to make claims about imminent election interference that paint a bleak picture of the current election season.

A recent article from The Hill relies on the acting head of DHS, Chad Wolf, as its only source, citing Wolf’s claim that “we fully expect Russia to attempt to interfere in the 2020 elections to sow public discord and undermine our democratic institutions” amid other warnings that Wolf gave about Chinese and Iranian cyber threats to U.S. elections. Other articles, including one titled “Russia, China plan to adjust their tactics to hack, influence 2020 elections” cite only Shelby Pierson of the U.S. intelligence community as its source for that headline’s claim. Another titled “Russia isn’t the only threat to 2020 elections, says U.S. intel” cites only anonymous U.S. intelligence officials, as the headline suggests.

Though Russia and China have consistently been named as the most likely election meddlers, reports have also been drumming up the likelihood that Iran will emerge as 2020’s foreign meddler of choice, especially in the months prior to and weeks after the killing of Iranian General Qassem Soleimani by the Trump administration. A recent “informal poll” conducted by the Washington Post asked hawkish think tank fellows, employees at companies like Raytheon and current and former federal officials if Iran would likely retaliate against the U.S. via cyberattack. The Post ran the results of the poll under the headline “Get ready for serious cyberattacks from Iran, experts say.”

Despite the media’s numerous warnings of imminent and “serious” cyber-retaliation from Iran, the only cyberattack attributed to the country after Soleimani’s death was the vandalism of the Federal Depository Library Program website, a rather benign act that was nevertheless blasted across headlines such as “US government website hacked with pro-Iranian messages, image of bloodied Trump.” The U.S. government is quoted in that article as saying that “At this time, there is no confirmation that this was the action of Iranian state-sponsored actors.”

Also notably absent from media reports is the fact that WikiLeaks revealed in 2017 that the CIA had stockpiled a library of “stolen” cyberattack techniques produced in other nations, including Russia and Iran. Those revelations, part of the Vault 7 release, revealed that the CIA’s UMBRAGE group was capable of “misdirect[ing] attribution [for cyberattacks actually done by the CIA] by leaving behind the ‘fingerprints’ of the groups that the attack techniques were stolen from.” In other words, the CIA was more than capable of conducting “false flag” cyber attacks and blaming them on foreign actors.

Notably, one of the viruses being blamed on Iran for cyberattacks targeting the U.S. ahead of the 2020 election — called Shamoon — was “stolen” by the CIA’s UMBRAGE and cited in the WikiLeaks release.


Conflict of interest-ridden Microsoft “defends democracy”

Last year saw the tech behemoth Microsoft join the effort to blame foreign state actors, specifically Iran, for cyberattacks against the U.S. This helped to bolster assertions that had largely originated with a handful of U.S. intelligence officials and hawkish, neoconservative-aligned think tanks as media reports on Microsoft’s related claims treated the company as an independent private sector observer.

Yet, as MintPress investigations have revealed, Microsoft has clear conflicts of interest with respect to election interference. Its “Defending Democracy” program has spawned tools like “NewsGuard” and “ElectionGuard” that it claims will help protect U.S. democracy, but — upon closer examination — instead have the opposite effect.

Last January, MintPress exposed NewsGuard’s neoconservative backers and how special interest groups were backing the program in an effort to censor independent journalism under the guise of the fight against “fake news.” Subsequent investigations revealed the risk that Microsoft’s ElectionGuard poses to U.S. voting machines, which it claims to make more secure and how the platform was developed by companies closely tied to the Pentagon’s infamous research branch DARPA and Israeli military intelligence Unit 8200.

ElecionGuard software has since been adopted by numerous voting machine manufacturers and is slated to be used in some Democratic Primary votes. Notably, the push for the adoption of ElectionGuard software has been spearheaded by the recently created Cybersecurity and Infrastructure Security Agency (CISA), which is the federal agency tasked with overseeing election security and is headed by Christopher Krebs, a former high level Microsoft executive.

In recent months, Microsoft has also been at the center of claims that Iran attempted to hack U.S. presidential campaigns ahead of 2020 as well as claims that Iran plans to target the U.S. power grid and other critical infrastructure with cyberattacks.

Last October, Microsoft penned a blog post discussing a “threat group” it named Phosphorus that they “believe originates from Iran and is linked to the Iranian government.” The post went on to claim that Phosphorus attempted to target a U.S. presidential campaign, which later media reports claimed was President Trump’s re-election campaign. Microsoft concluded that the attempt was “not technically sophisticated” and ultimately unsuccessful, but felt compelled to disclose it and link it to Iran’s government.

Though it provided no evidence for the hack or its reasons for “believing” that the attack originated from Iran, media reports treated Microsoft’s declaration as proof that Iran had begun actively meddling in the 2020 election. Headlines such as “Iranian Hackers Target Trump Campaign as 2020 Threats Mount,” “Iran-linked Hackers Target Trump 2020 Campaign, Microsoft says”, “Microsoft: Iran government-linked hacker targeted 2020 presidential campaign” and “Microsoft Says Iranians Tried To Hack U.S. Presidential Campaign,” were blasted across the front pages of American media. None of the reports scrutinized Microsoft’s claims or noted the clear conflict of interest Microsoft had in making such claims due to its efforts to see its own ElectionGuard Software adopted nationwide.
Media reports also left out the fact that Microsoft is a major government contractor for the U.S. intelligence community and the Pentagon. Notably, the Trump campaign, which Microsoft said was the target of this attack, was later identified as the only major presidential campaign using Microsoft’s “AccountGuard” software, part of its dubious “Defending Democracy” program that also spawned NewsGuard and ElectionGuard. AccountGuard claims to protect campaign-linked emails and data from hackers.

Microsoft surfaced not long after, again claiming that Iran was maliciously targeting the United States’ civilian infrastructure. This subsequent claim was first published by Wired and later covered by other outlets. Those reports cite a single person, Microsoft security researcher Ned Moran, who claimed that an Iran-backed hacking group called APT33 was targeting the U.S. “physical control systems used in electric utilities, manufacturing, and oil refineries.”

“They’re trying to deliver messages to their adversaries and trying to compel and change their adversaries’ behavior,” Moran told Wired. Moran also stated that “Microsoft hasn’t seen direct evidence of APT33 carrying out a disruptive cyberattack rather than mere espionage or reconnaissance, it’s seen incidents where the group has at least laid the groundwork for those attacks (emphasis added).”


Cybereason helps craft the narrative

While U.S. intelligence officials and media outlets alike have been largely responsible for setting the narrative that imminent meddling will be conducted by Russia, China and Iran, key components of that narrative, particularly with respect to China and Iran, have been laid by Cybereason, a company that recently ran 2020 doomsday election simulations and that has close ties to the intelligence communities of both the U.S. and Israel.

Shortly after the killing of Iranian General Qassem Soleimani earlier this month, an operation conducted in concert with Israeli intelligence, Cybereason warned that Iran could imminently retaliate with a cyber threat and quoted its own employees who explained what and how Iran would likely target in retaliation. Cybereason’s CSO Sam Curry, who actively participated in the firm’s 2020 doomsday election simulations, stated:

 This means that Iran’s “forceful revenge” response is likely to be less about the flash and all about the bang. If you have connected systems that are responsible for kinetic world effects, like ICS systems and critical infrastructure around water, energy or vital services, it’s time to pay attention. Iran and the US are engaged in Cyber brinksmanship, which means that the gloves are off as Iran picks it’s targets (emphasis added).”

Cybereason also quoted visiting fellow for the National Security Institute and former advisor to the U.S. Secret Service (which participated in Cyberaeson’s election simulations), Anne Marie Zettlemoyer, who claimed that Iran could soon target Wall Street and critical U.S. infrastructure like the power grid:

 An attack against the financial systems can be devastating economically and weaken the confidence and viability of markets. However, we cannot ignore the physical consequences and manifestations that can come from a cyberattack, particularly against critical infrastructure like energy and industry control systems.”

Cybereason’s claims regarding Iran’s interest in “critical infrastructure” systems likely originated with Microsoft, the claims were then parroted by the media in several reports, many of which quoted Cybereason’s Sam Curry. Curry is also a contributor to major news outlets like Forbes where he writes about Iran’s cyber warfare capabilities.

Notably, in Cybereason’s recent allegations against Iran, it states that “it’s clear that Iran has been preparing for future geopolitical conflict by gaining access to critical infrastructure and other important operations in the United States.” It backs these claims by citing an article authored by Curry for Forbes. Following Soleimani’s death, numerous media reports, including in the UK’s The Independent and ABC News, have cited Curry as an “expert” source in claiming that Iran would retaliate with cyberattacks.

Microsoft’s claims about foreign hackers and meddling — the evidence for which have never been made public but has been parroted as fact nonetheless — are frequently supported by Cybereason.

Last August, Microsoft claimed to have foiled Russian attempts at hacking two Republican-affiliated think tanks and, despite providing no evidence, Cybereason’s then-senior director of intelligence services Ross Rustici was quoted as an expert in several media reports as saying that such behavior was to be expected from Russia. In one such report, Rustici stated:

We’re very good at fighting the last war, but the Russians are very good at evolving their game. I suspect if they’re going to do a psychological operation around the elections, the way they do it will be different than what they did in 2016. How effective the defenses we’ve built for what they did in 2016 will be for those attacks is yet to be seen.”

None of the media reports quoting Rustici mentioned Cybereason’s ties to Israeli intelligence, referring to tech firms only a “Boston-based cybersecurity company” and similar variants. Cybereason’s Intelligence Group is stuffed with former and active members of U.S. and Israeli intelligence services and has released several reports about nation-state hacking with a focus on Russia and China.

Cybereason has also been at the forefront of claims that China has been engaged in aggressive cyberattacks against multinational companies that have also seen widespread coverage in U.S. media, despite the untransparent nature of the evidence for Cybereason’s claims.

In a story that received major coverage from outlets such as Fox News, Reuters, CNBC and others, Cybereason unveiled what it called “Operation Soft Cell,” an operation that stole mass troves of data from several global telecommunications companies. In each story, Cybereason is the sole source of the claim and declined to provide the name or location of any of the affected companies. The firm also claimed to have determined that the attack was likely perpetrated by someone “backed by a nation state, and is affiliated with China.” It further claimed to have debriefed and coordinated responses with U.S. intelligence.

In an article for Reuters, Cybereason stated that “this time as opposed to in the past we are sure enough to say that the attack originated in China” while Cybereason separately told CyberScoop that it had “found hacking tools such as a modified web shell and a remote access trojan that are commonly associated with, but not unique to, Chinese hackers.” Despite the incongruity, media reports laid the blame squarely on China, as seen in headlines such as “Chinese spies have been sucking up call records at multinational telecoms, researchers say.”

Prior to uncovering Operation Soft Cell, Cybereason had warned on its blogs in the months and years prior that China would imminently target U.S. companies. The revelation of Operation Soft Cell — which originated exclusively with Cybereason — has been used to build the case that China is openly engaged in cyberwarfare against its rival states, like the United States, and targeting “democracy itself.”


Best Known Deep Fake Creator is Funded by Israeli Intelligence

While the media, and even Cybereason itself, have helped lay the foundation to blame specific state actors for 2020 election meddling well ahead of the fact, it is worth revisiting Cybereason’s “Operation Blackout” election simulation and the tactics used by the “bad actors” in that scenario.

That simulation, discussed in detail in the first installment of this series, saw the weaponization of specific technologies, namely deep fakes, hacks of Internet of Things (IoT) devices and hacks of vehicles, in order to target the 2020 U.S. election, resulting in the cancellation of the election and the imposition of martial law.

Given the current narrative regarding what state actors are likely to meddle in the 2020 election — namely Russia, China and Iran — and the tactics they will allegedly use, it is important to explore the sources of the technologies weaponized per that narrative as well as in “Operation Blackout.”

Indeed, if there is any clear overlap between the creators of those technologies and the state actors being blamed in advance for their imminent use, it would certainly lend credibility to the claims promoted by U.S. intelligence, the media and companies like Microsoft and Cybereason.

Yet, upon closer examination, it becomes clear that the companies and state actors most involved in developing these technologies are the very ones claiming that Russia, China and Iran will use them to undermine the 2020 election.

Take for instance the use of deep fakes. Not only have numerous media reports focused on how deep fakes will be used to meddle in the 2020 elections, but Cybereason’s doomsday election simulation saw “bad actors” rely heavily on their use to spread disinformation and even make fake bomb threats. While much has been said of the coming election and deep fakes, remarkably few reports have bothered to look at the company best known for creating viral deep fakes.

Canny AI has garnered considerable media attention over the past few years for its persuasive deep fake videos that have frequently gone viral. In the last year alone, the tech firm’s viral deep fakes have included a controversial video of Mark Zuckerberg where the Facebook co-founder appears to be saying “Imagine this for a second: One man, with total control of billions of people’s stolen data, all their secrets, their lives, their futures,” as well as a video showing Richard Nixon giving a speech he never actually gave. More recently, Canny AI was behind the viral videos immediately prior to the 2019 U.K. general election that appeared to show Jeremy Corbyn and his rival Boris Johnson endorsing each other and another video that showed world leaders singing John Lennon’s “Imagine”:

Oddly, many of the media reports that discuss these viral videos fail to mention the role of Canny AI in creating these viral deep fakes and instead only mention the organization or artists with whom Canny AI partnered to create them. For instance, the Corbyn-Johnson videos were reported to have been produced by the group Future Advocacy and artist Bill Posters, but it was actually Canny AI that created those videos for that group. Similarly, the Nixon Speech deep fake was reported by several outlets as having been solely created by MIT’s Center for Advanced Virtuality. However, the Boston Globe noted that “the [MIT] team worked with Canny AI, an Israeli company that does Video Dialogue Replacement, and Respeecher, a Ukrainian startup specializing in speech-to-speech synthetic voice production” to create the video.

The Zuckerberg deep fake that Canny AI created led to lots of positive press for the company, with several media reports dubbing them as the company using “deep fakes for good” and that uses the controversial technology “responsibly.” The Zuckerberg deep fake has been cited as one of the main drivers behind Facebook’s new “deep fake” policy, which only bans some deep fake videos and has been criticized by U.S. lawmakers as insufficient. Notably, neither Facebook nor Facebook-owned Instagram ever took down Canny AI’s deep fake of Zuckerburg.

Given the concern over deep fakes in relation to the coming election and Canny AI standing out as the main producer of deep fakes that have gone viral over the past year, it is important to point out that Canny AI has ties to a state actor with a history of election meddling: the state of Israel.

Indeed, Canny AI is 100 percent funded by an Israeli start-up accelerator called Xcelerator, a joint venture between Tel Aviv University and Israeli intelligence agency Shin Bet (sometimes called Shabak). According to Start Up Nation Central, the Paul Singer-created organization that promotes Israeli technology start ups, Xcelerator-funded “start-ups participating in the program benefit from close mentoring from content and technology experts from the Shabak, experts from Tel Aviv University, and industry leaders. The connection to the Shabak also provides the entrepreneurs with ways to test the capabilities of their technologies and cooperation opportunities (emphasis added).”

In addition, Xcelerator is partnered not only with Israeli intelligence directly, but also with Cybereason, the very company that explored the use of deep fakes in the 2020 U.S. presidential election that saw the election cancelled and martial law declared as well as a company that itself has deep ties to Israeli intelligence. Other notable partners of Xcelerator include NEC Corp, which has intimate ties to top Cybereason investor Softbank; Check Point Technologies, which has ties to Israeli military intelligence Unit 8200; and the Israeli start-up accelerator Team8. In previous reports published by MintPress, Team8 was discussed in detail, particularly their recent hire of former director of the NSA and former head of U.S. Cyber Command Mike Rogers, and their close ties to Paul Singer’s Start Up Nation Central, which itself has deep ties to U.S. neoconservatives.

It is also worth noting that Xcelerator also backs an “anti-fake news” start-up called Cyabra, which has direct ties to Israel’s Mossad and offers its AI-driven “disinformation protection” to government agencies as well as politicians, particularly during election seasons. Two of Cyabra’s co-founders previously co-founded Psy-Group, which attempted to interfere in the 2016 U.S. election by weaponizing “fake news” and social media and later closed down its operations after U.S. government scrutiny into its activities began as part of the Mueller investigation.

Psy-Group also engaged in doxxing campaigns targeting Palesintian rights activists in the U.S. which were planned in conjunction with Ram Ben-Barak, the former deputy director of the Mossad who now advises Cyabra. Given that much of the concern ahead of the next election is related not only to deep fakes but also “fake news,” Cyabra’s rise and its clear ties to Mossad and the now defunct Psy-Group are important to note.

Furthermore, in examining the other technologies weaponized during Cybereason’s 2020 election simulation and cited in the aforementioned media narrative regarding 2020 meddling, a pattern similar to that of Canny AI emerges.

Indeed, the other technologies linked to these “bad actors” and foreign meddlers — namely hacking IoT devices and hacking vehicles — are also pioneered by companies with deep ties to Israeli military intelligence, specifically Unit 8200, and Israeli tech companies that have aggressively spied on U.S. government institutions in collusion with Israeli intelligence in the past, namely Comverse (now Verint) and Amdocs.


Hacking the Internet of Things

In Cybereason’s doomsday election simulation, another of the tactics used was the hacking of devices and appliances connected to the internet, often referred to as the Internet of Things (IoT) and which includes everything from smartphones to power grid infrastructure to city traffic lights.

While most reports on IoT hacks to date have focused on “lone wolf” or non-state-aligned actors, one company has stood out for its efforts to create a tool that would allow governments and intelligence agencies to hack these devices with ease. That company, called Toka, announced in 2018 that it planned to offer “a one-stop hacking shop for governments that require extra capability to fight terrorists and other threats to national security in the digital domain,” with “a special focus on [hacking] the so-called Internet of Things (IoT), covering tech like Amazon Echo, Nest connected home products, as well as connected fridges, thermostats and alarms.”

The Israel-based company, which raised $12.5 million within months of launching, has since been busy marketing its services to governments around the world, most recently France where it described its product portfolio as “empower[ing] governments, Intelligence, and law enforcement agencies to enhance Homeland Security with groundbreaking cyber-intelligence and operational capabilities” during an exposition in Paris last November.

Even though Toka openly markets the ability to hack private consumer devices to governments and law enforcement agencies around the world, the clear threat to privacy has gone ignored by media outlets as the company has garnered nearly no media attention since it launched nearly two years ago.

Yet, Toka is not only notable for what it offers but also for its founders and investors. Indeed, the co-founders of Toka have been described as an “all-star” team, largely because of the role of former Israeli Prime Minister and former head of Israeli military intelligence, Ehud Barak. Barak, in addition to co-founding the company, serves as its director and is also the chairman of the board of the controversial Israeli company Carbyne911, which markets software to emergency call centers in the United States. Interestingly, Cybereason’s 2020 doomsday election simulation also dealt with the hacking and weaponization of 911 call centers. Also of note is the fact that another of Carbyne911’s leadership team, former Unit 8200 commander Pinchas Buchris, is an adviser to Cybereason.
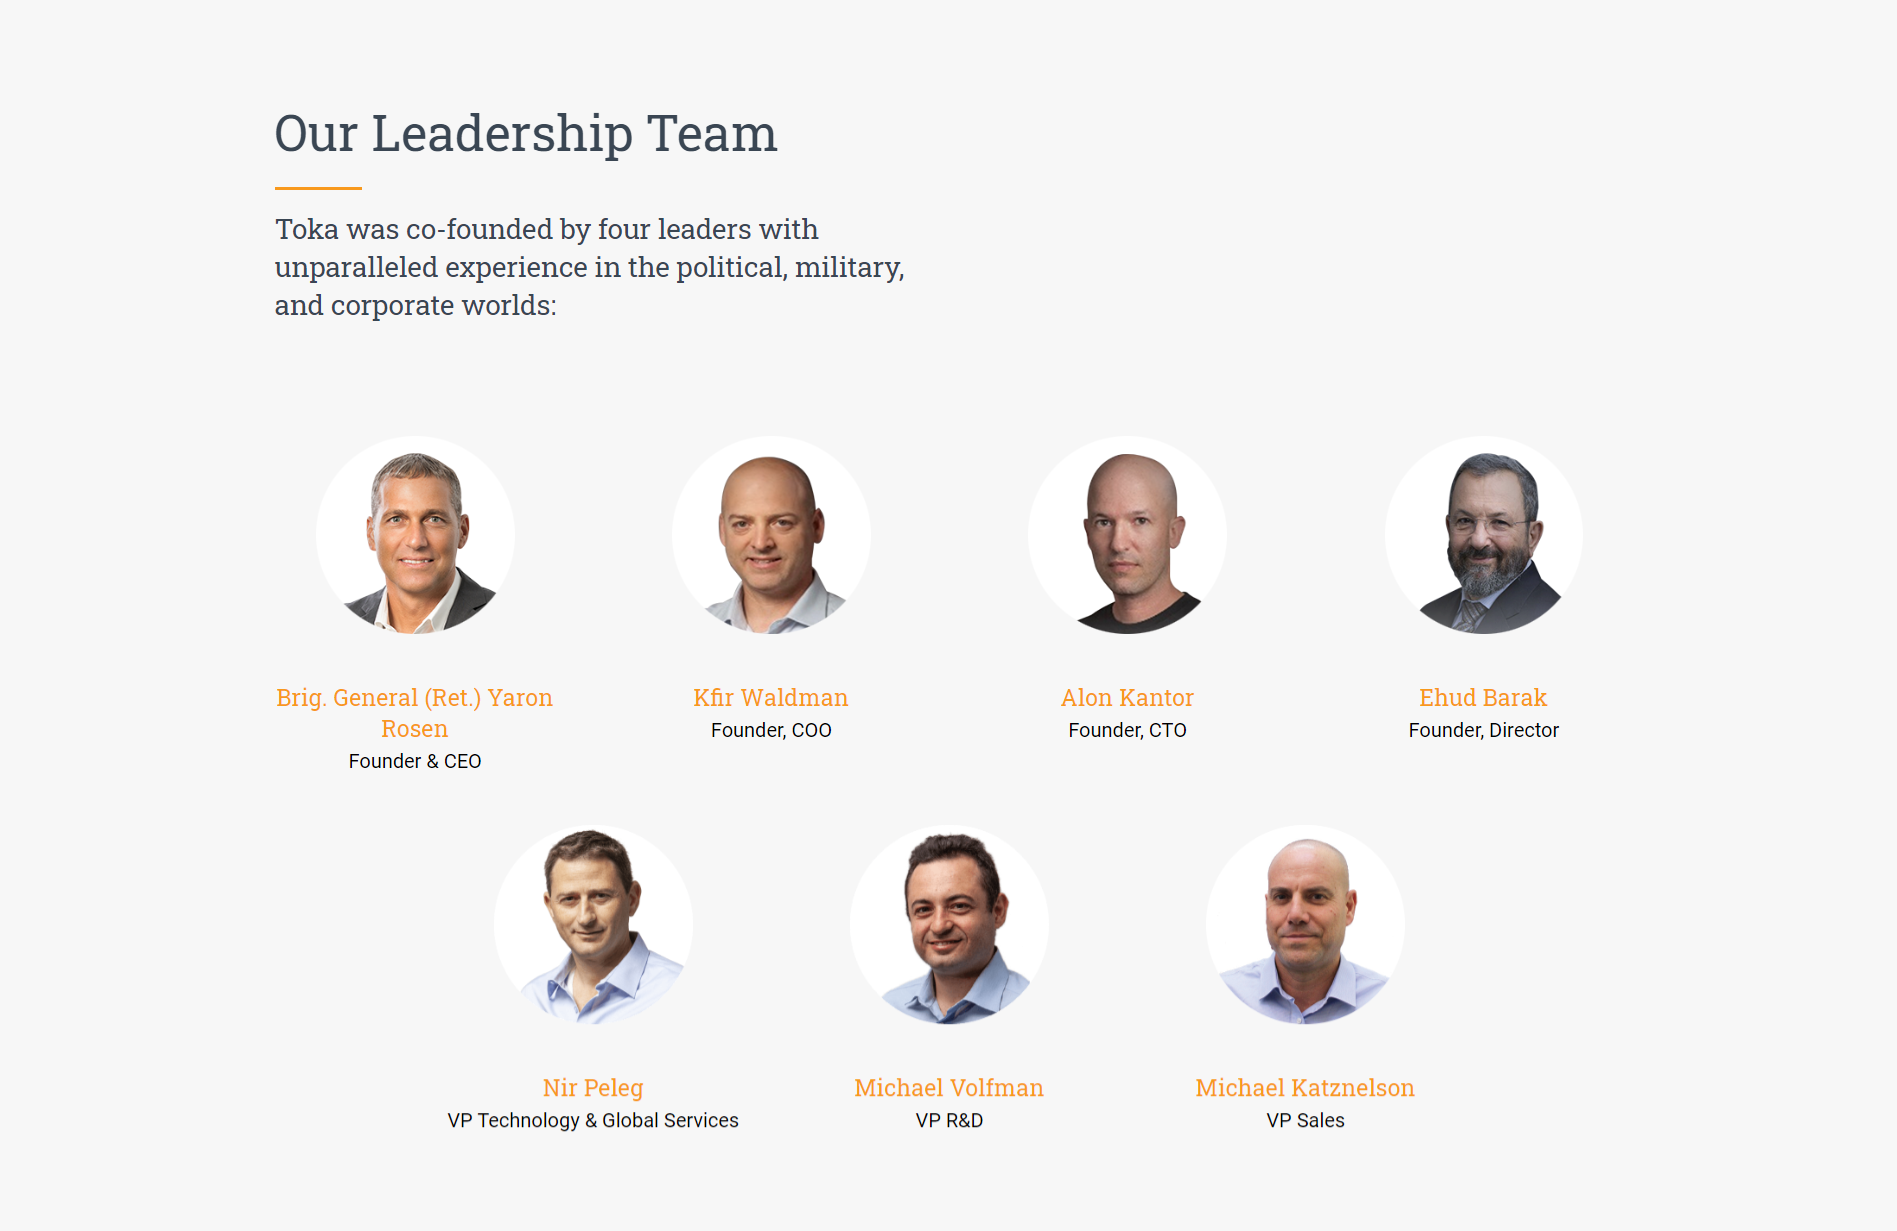
Toka Leadership team

In addition to Barak, Toka was co-founded by retired Brigadier General Yaron Rosen, former Chief of the IDF’s cyber staff, where he was “the lead architect of all [IDF] cyber activities” including those executed by Israeli military intelligence Unit 8200. Rosen, who now serves as Toka’s CEO, has stated that Toka’s technology will only be sold to countries allied with the U.S. and Israel, telling Forbes that “Russia, China and ‘other enemy countries’ would never be customers.”

Toka’s leadership and software architects are similarly tied into Israel’s national security state. Several — including the “architect” of its hacking software — previously worked for Israel’s Prime Minister’s Office and developed “offensive technologies” for Israel’s head of state and other top Toka employees and executives share numerous connections to Unit 8200, other divisions of Israeli military intelligence and Unit 8200-connected tech companies like Check Point Technologies.

Though Toka’s leadership team makes its ties to Israeli military intelligence abundantly clear, important connections also appear in examining Toka’s investors. One of the major investors in Toka is Dell technologies, one of the world’s largest technology companies that was founded by Michael Dell, a well-known pro-Israel partisan who has donated millions of dollars to the Friends of the IDF and one of the top supporters of the so-called “anti-BDS” bills that prevent publicly employed individuals or public institutions from supporting non-violent boycotts of Israel, even on humanitarian grounds. It goes without saying that a major technology company investing in a company that markets the hacking of that very technology (computers, IoT, smartphones, etc.) should be a red flag.

With a major foot in the door through its connections to Dell, whose products are used by the private and public sectors around the world, other investors in Toka again reveal its ties to Israel’s military intelligence and the same controversial Israeli tech companies that have aggressively spied on the U.S. government in the past — Amdocs and Comverse. For instance, Entrèe Capital, a venture capital fund that is one of Toka’s main investors, is managed by Aviad Eyal and Ran Achituv. The latter, who manages Entrée’s investment in Toka and sits on Toka’s board of directors, is the founder of the IDF’s satellite-based signals intelligence unit and also a former senior Vice President at both Amdocs and Comverse Infosys (Verint).

Another notable investor in Toka is the venture capital firm Andreesen Horowitz, which is advised by former Secretary of the Treasury Larry Summers, a close friend of the infamous pedophile Jeffery Epstein, whose own ties to Israeli military intelligence have been discussed in several MintPress reports. Epstein was also a close friend of Ehud Barak, co-founder and director of Toka, and invested at least $1 million in another company with close ties to Barak, Carbyne911. The remaining investors in Toka are Launch Capital, which is deeply tied to the Pritzker family — one of the wealthiest families in the U.S. with close ties to the Clintons and Obamas as well as the U.S.’ pro-Israel lobby, and Ray Rothrock, a venture capitalist who spent nearly three decades at VenRock, the Rockefeller family venture capital fund.


Unit 8200 – From Hacking Cars to Protecting Them?

Arguably the most disturbing aspect of Cybereason’s “Operation Blackout” election simulation was the hacking of vehicles that were then rammed into civilians waiting in line to vote at polling stations. In the simulation, this led to scores of dead Americans and hundreds of injuries.

As was the case with other technologies used to undermine the 2020 election in the simulation, this technology — the hacking of vehicles — is the bread and butter of an Israeli cybersecurity firm called Upstream Security that specializes in automobiles and boasts deep ties to the country’s military intelligence service.

Though vehicle hacking seemed out of left field when the 2020 election simulation took place last November, media reports about the imminent dangers of “car hacking” began to emerge just a month after the exercise took place, most of which cited a December 2019 report created by Upstream. Some of those reports have warned that car hacking could be used to undermine the coming U.S. election.

One report titled “Car Hacking Hits the Streets,” cites only Upstream’s report to claim that “In 2020, the connected-car market will reach a tipping point, with the majority of vehicles already connected to the Internet when sold in the United States, representing a large base of potential targets for attacks.” Another report, titled “New study shows just how bad vehicle hacking has gotten,” uses Upstream’s report (i.e. study) to claim that hacks of regular vehicles have exploded since 2016 and that most of the cars on U.S. roads today are vulnerable to hackers and that over 80 percent of those hacks occur remotely.

Neither report noted Upstream’s ties to Israeli military intelligence. Equally notable is the fact that both reports that covered the Upstream-written study say that only manufacturers can address the problem by partnering with a company like Upstream.
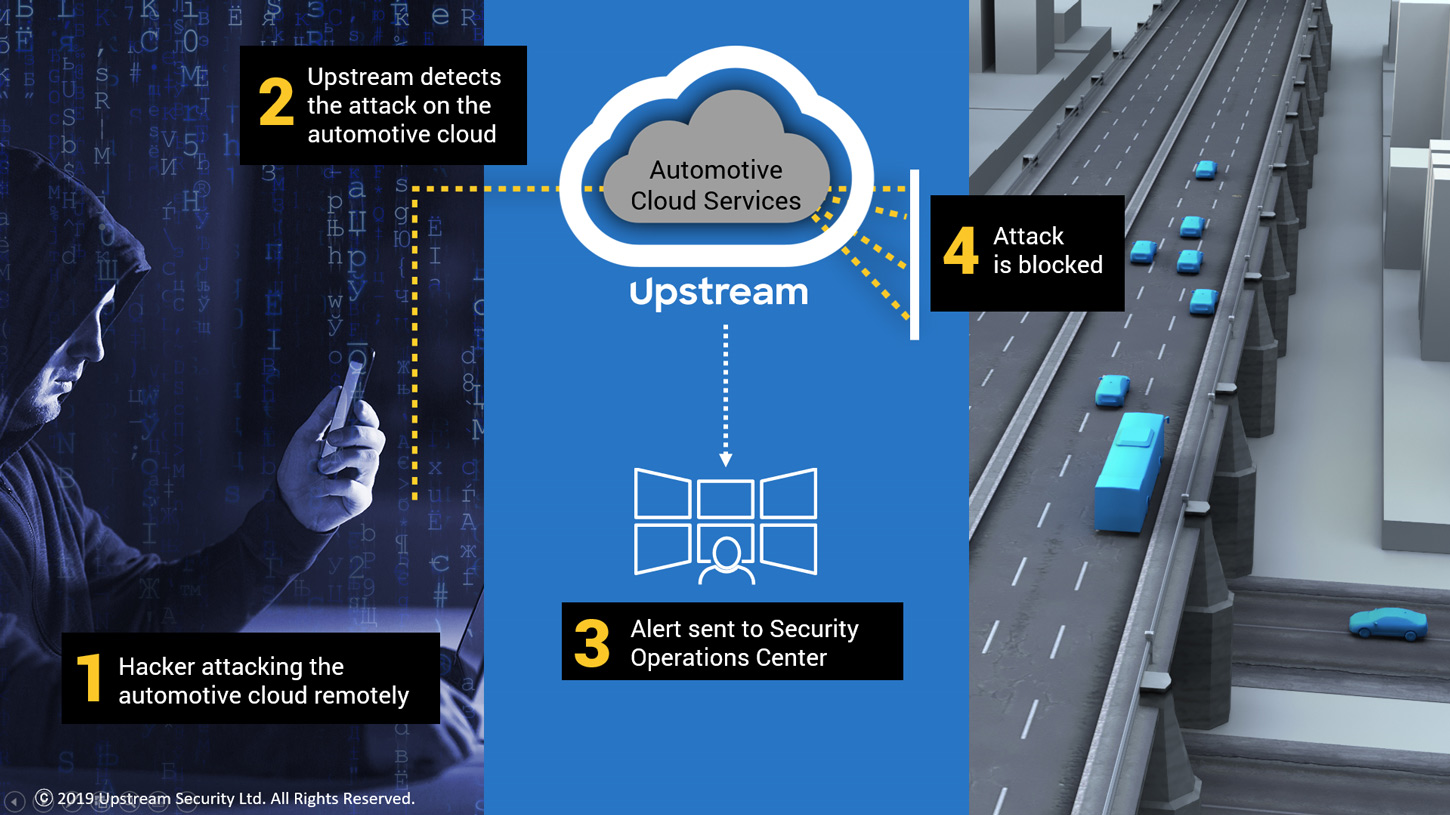
Upstream promo

Lucky for Upstream, they have already partnered with a slew of auto manufacturers, including Hyundai, Volvo, Renault and even U.S. auto insurance giants like Nationwide, who now number among Upstream’s most important investors. The company’s original investors are Charles River Ventures, one of Cybereason’s first investors, and Israeli venture capital firm Glilot Capital.

Glilot Capital’s interest in Upstream is telling given the firm’s deep ties to Israel’s Unit 8200. Glilot was founded by two former Israeli military intelligence officers and has “a heavy focus on the cyber sector and the entrepreneurs who emerge from the elite Unit 8200,” according to the Jerusalem Post. Even the name of the firm is an homage to Unit 8200, as the unit’s main base is located in Glilot, near Herzliya.

“It’s as if Americans called a VC Fort Meade Capital [the US Army base in Maryland where the National Security Agency and the United States Cyber Command are headquartered], some VC names are meant to be symbolic, as in our case. Glilot is the home of several of the best intelligence and technology units in the IDF, it’s where we came from and it is where we find our best entrepreneurs,” Glilot Capital co-founder Arik Kleinstein told the Jerusalem Post in 2016.

Upstream is certainly the type of company that Glilot Capital is used to investing in. It was founded by two Israelis who both served in the IDF, with one of them serving in an elite intelligence unit. Upstream’s co-founders, Yoav Levy and Yonathan Appel, met while working at Check Point Technologies, the Unit 8200 alumni-founded company with deep ties to Israel’s military intelligence and military-industrial complex as well as the IoT hacking company Toka. Notably, Upstream recently partnered with the Japanese company Fujitsu, a longtime partner with Softbank — Cybereason’s main investor.

Softbank has also invested heavily in another Unit 8200-founded vehicle security start-up called Argus Cyber Security, a firm known for its numerous demonstrations showing how easy it is to hack vehicles. Argus is also backed by Nadav Zafrir, the former Unit 8200 commander who now runs Team8. Argus’ CEO Ofer Ben-Noon, a former captain in Unit 8200, told Forbes in 2014 that “Everything will be hacked in every single [car] brand. It will take time, it might be weeks, months, or a couple of years, but eventually it will happen.”

Since then, Unit 8200 alumni from Argus, Upstream and other Israeli automobile cybersecurity firms have shown media outlets around the world how much easier hacking vehicles has become in the years since Ben-Noon first made the claim. One such report from VICE includes a vehicle hacking demonstration, courtesy of a Unit 8200 alumni, and notes that “most cars today are susceptible to hacker attacks.”

Of course, Unit 8200 isn’t the only intelligence agency known to be experts at hacking vehicles. Indeed, in 2017, WikiLeaks revealed that the CIA was capable of hacking vehicles and exploring their use in committing “undetectable assassinations.”


“Bring down nations to their knees”

At the Tel Aviv Cybertech Conference in 2017, Israeli Prime Minister Benjamin Netanyahu stated the following:

Today warfare has changed dramatically…With a click of a button, you can bring down nations to their knees very rapidly if you so desire and if you’re willing to take the risks, because every system can be hacked. Our hospitals, our airplanes, our cars, our banks. The most important word here is our data banks, they can be hacked.”

Media reports and even members of the Israeli public and private sector have openly acknowledged that Israel’s intelligence apparatus — from Unit 8200 to the Mossad — remains directly linked to many of the private technology companies founded by its former members, especially in the field of cybersecurity. Though reports on the matter often praise this merging of Israel’s public and private spheres, they rarely acknowledge the documented corruption within Unit 8200, the unit’s dark past in recruiting felons and even pedophiles to join its ranks, or the danger posed by having companies directly linked to foreign intelligence being given access to the U.S. government’s most classified and sensitive systems and data.

The last omission is particularly troubling given that Israeli intelligence has not only been caught aggressively using private tech companies to spy on U.S. federal agencies and networks, but also intercepting the private communications of at least two U.S. presidents and using a notorious pedophile to sexually blackmail American politicians.

As was mentioned in the first installment of this series, Cybereason’s CEO Lior Div offers a clear example of this worrisome bridge between Israel’s public and private sector, as Div has openly stated that he views his work at Cybereason as a “continuation” of his service to Israeli military intelligence, where he led offensive cyberattacks against other nations.

Given Div’s past statements and his company’s clear ties to both Israeli and U.S. intelligence, Cybereason’s simulation of the 2020 U.S. election — which involved terrorist attacks and led to the election’s cancellation and the imposition of martial law — is highly concerning. This is particularly so considering that Cybereason’s investors have direct ties to individuals who would benefit from the election’s cancellation and also considering the clear narrative that has emerged in recent months regarding how the coming election will inevitably fall victim to tech-driven “chaos” in coming months.

The clear overlap between Cybereason’s simulation and the intelligence-driven media narrative is clear cause for concern, especially considering that the technologies that they highlight as ultimately upending the election are dominated by the very same intelligence agencies simulating and crafting that narrative.

The keyword that has been used to describe the end result of both Cybereason’s simulation and the prevailing media narrative regarding the 2020 election is “chaos,” chaos so imminent, widespread and unruly that it will shake American democracy to its core.

What has been left unsaid, however, is that a government’s solution to “chaos” is always the imposition of “order.” This means that — whatever “chaos” ultimately ensues prior to or on election day — will result in a government response that will do much more to crush freedom and undermine democracy than any act of foreign meddling has, be it real or imagined.
Republish our stories! MintPress News is licensed under a Creative Commons Attribution-NonCommercial-ShareAlike 3.0 International License.

Be seeing you

Chad


Posted in Uncategorized | Tagged: , , , , , | Leave a Comment »

The Primary Mechanism Of Your Oppression Is Not Hidden At All – Caitlin Johnstone

Posted by M. C. on February 3, 2020

…we see not public accountability, nor demands for sweeping systemic changes to prevent such malfeasance from reoccurring, but a bunch of narrative management from the political/media class.

This narrative management is used to shift attention away from the information that was revealed and onto the fact that the person who revealed it broke the law or misbehaved in some way. It’s used to convince people that the revelations aren’t actually a big deal, or that it was already basically public knowledge anyway.

https://caitlinjohnstone.com/2020/02/02/the-primary-mechanism-of-your-oppression-is-not-hidden-at-all/

I write a lot about government secrecy and the importance of whistleblowers, leakers and leak publishers, and for good reason: governments which can hide their wicked deeds from public accountability will do so whenever possible. It’s impossible for the public to use democracy for ensuring their government behaves in the way they desire if they aren’t allowed to be informed about what that behavior even is.

These things get lots of attention in conspiracy circles and dissident political factions. Quite a few eyes are fixed on the veil of government opacity and the persecution of those brave souls who try to shed light on what’s going on behind it. Not enough eyes, but quite a few.

What gets less attention, much to our detriment, is the fact that the primary mechanism of our oppression and exploitation is happening right out in front of our faces.

The nonstop campaign by bought politicians, owned news outlets, and manipulated social media platforms to control the dominant narratives about what’s going on in the world contribute vastly more to the sickness of our society than government secrecy does. We know this from experience: any time a whistleblower exposes secret information about the malfeasance of powerful governments like NSA surveillance or Collateral Murder, we see not public accountability, nor demands for sweeping systemic changes to prevent such malfeasance from reoccurring, but a bunch of narrative management from the political/media class.

This narrative management is used to shift attention away from the information that was revealed and onto the fact that the person who revealed it broke the law or misbehaved in some way. It’s used to convince people that the revelations aren’t actually a big deal, or that it was already basically public knowledge anyway. And it’s used to manipulate public attention on to the next hot story of the day and memory hole it underneath the white noise of the media news churn. And nothing changes.

We’ve seen it happening over and over and over again. The narrative management machine has gotten so effective and efficient that it’s been able to completely ignore the recent revelation that the US, UK and France almost certainly bombed Syria in 2018 for a completely false reason. A few half-assed Bellingcat spin jobs and an otherwise total media blackout, and it’s like the whole thing never happened.

What this tells us is that our first and foremost problem is not the fact that conspiracies are happening behind a curtain of government secrecy, but that the way people think, act and vote is being actively manipulated right out in the open. Government secrecy is indeed one aspect of establishment narrative control, but controlling the public’s access to information is only one aspect. The bigger part of it is controlling how the public thinks about information.

The reason people never use the power of their superior numbers to force real change, even though they’re being exploited and oppressed in myriad ways by the ruling class, is because they’ve been propagandized into accepting the status quo as desirable (or at least normal). The propaganda of the political/media class is therefore the establishment’s front line of defense. Its most powerful, and essential, weapon.

This is important for dissidents of all stripes to understand, because it means we’re not just passively waiting around for another Manning or Snowden or an Ian Henderson to give us information which we can use to fight the oppression machine. Those individuals have done a great public service, but the battle to awaken human consciousness to what’s really going on in our world is in no way limited to leakers and whistleblowers. It is not at the mercy of government secrecy.

If you are engaged in any type of media, you are engaging the narrative matrix which keeps the public asleep and complacent. It doesn’t matter if you have a Twitter account, a Youtube account, some flyers or a can of spray paint: if you are capable of getting any kind of message out there, you are able to directly influence the mechanism of your oppression. You are able to inform people that they are being lied to, you are able to explain why, and you are able to point them to where they can find more information.

This is extremely empowering. You do not need to wait around hoping that some bombshell piece of information makes it past all the various security checks and spinmeisters and triggers a real social awakening. You can be that information. You can become a catalyst for that awakening.

The key to turning this ship around does not lie hidden somewhere behind a veil of government opacity. It lies in you. It lies in all of us. We can begin awakening our fellow humans right now by attacking the narrative management of the propaganda machine that sits right in front of us, unarmored and unhidden.

____________________________

Thanks for reading! The best way to get around the internet censors and make sure you see the stuff I publish is to subscribe to the mailing list for my website, which will get you an email notification for everything I publish. My work is entirely reader-supported, so if you enjoyed this piece please consider sharing it around, liking me on Facebook, following my antics on Twitter, checking out my podcast on either Youtube, soundcloud, Apple podcasts or Spotify, following me on Steemit, throwing some money into my hat on Patreon or Paypal, purchasing some of my sweet merchandise, buying my new book Rogue Nation: Psychonautical Adventures With Caitlin Johnstone, or my previous book Woke: A Field Guide for Utopia Preppers. For more info on who I am, where I stand, and what I’m trying to do with this platform, click here. Everyone, racist platforms excluded, has my permission to republish or use any part of this work (or anything else I’ve written) in any way they like free of charge.

Be seeing you

Posted in Uncategorized | Tagged: , , , , , | Leave a Comment »

IAN BIRRELL on how tech giants have turned San Francisco into a dystopian nightmare | Daily Mail Online

Posted by M. C. on February 3, 2020

Considering the city’s wealth, it smacks of callous and uncaring hypocrisy.

I had just passed dealers selling drugs beside a police car parked outside government offices

As one local resident says: ‘Are they really being progressive to that poor guy in the street with a needle in his arm who is going to die tomorrow?’

Here is a thought. Raise the minimum to guarantee these poor people will never get a job.

https://www.dailymail.co.uk/debate/article-7956517/IAN-BIRRELL-tech-giants-turned-San-Francisco-dystopian-nightmare.html

By Ian Birrell for The Mail on Sunday

Gilles Desaulniers moved to San Francisco 40 years ago, settling in the ‘friendly, quaint and affordable’ city after running out of cash while driving from Canada down the West Coast of America.

Today he runs a grocery store filled with fresh fruit, vegan snacks and organic wines typical of this famously liberal Californian city.

But Gilles has shut one outlet and would sell up entirely if anyone wanted this one, his remaining shop.

Each day, up to 30 people stroll in and openly steal goods, costing him hundreds of dollars.

A street cleaner showed me a box filled with used syringes that he had collected, then I met two charity workers picking up needles from the pavement. How many do you find a day, I ask? ¿Between 300 and 600, depending on the weather,¿ one replies. A homeless man is pictured second left using a syringe to inject drugs in the city in June 2018

A street cleaner showed me a box filled with used syringes that he had collected, then I met two charity workers picking up needles from the pavement. How many do you find a day, I ask? ‘Between 300 and 600, depending on the weather,’ one replies. A homeless man is pictured second left using a syringe to inject drugs in the city in June 2018

He has been bitten twice recently by people in his shop and he also found a woman turning blue in the toilet after a drugs overdose, a hypodermic needle still stuck in her leg.

He showed me a metal door that is corroding due to people urinating in his doorway, then spoke of finding a man relieving himself in full view of infants playing in a child centre next door.

‘Our society is falling apart,’ says Desaulniers.

‘If people do not play by some rules, society does not function. But it feels like there is no order, there is no shame.’

He uses two apocalyptic movies to illustrate the state of his adopted city: ‘Living here feels like A Clockwork Orange and Blade Runner have both come true.’

I could grasp his despair. I had just passed dealers selling drugs beside a police car parked outside government offices, and seen their customers openly smoke fentanyl, an opioid 50 times stronger than heroin, then collapse on the street…

Yet true to form, San Francisco has just elected as district attorney a radical called Chesa Boudin, whose parents were infamous militants from a far-Left, anti-war group. They were jailed for triple murder when Chesa was a toddler, leaving him to be adopted by the founders of the organisation.

The 39-year-old, who studied at Oxford University as a Rhodes scholar and later worked as a translator for Venezuela’s former leader Hugo Chavez, a Fidel Castro acolyte, campaigned on moving away from prosecuting ‘quality of life’ offences to focus on serious and corporate offences.

The San Francisco Police Officers Association spent heavily campaigning against Boudin, saying he was the choice for ‘criminals and gang members’.

But Jennifer Friedenbach, executive director of the charity Coalition on Homelessness, argues city residents should get angry over ‘systemic neglect’ that sparked this crisis rather than blaming people on the streets.

‘No one wants to live like this,’ she says. ‘We’ve tried locking people up before but that didn’t work.’

Friedenbach insists that the problems stem from a lack of affordable housing, a significant reduction of emergency shelters and the slashing of spending on treatment programmes.

She says, rightly, that issues of homelessness, mental health and addiction are often linked.

The city’s mayor, London Breed, whose younger sister died of a drug overdose and elder brother was jailed for robbery, declined to comment.

In her inaugural speech, Breed said the ‘twin troubles of homelessness and housing affordability’ were the big challenge.

She is boosting grants for shelters, treatment and street cleaning. Yet those desperate sights staining this one-time hippy nirvana are ultimately the sign of abject political failure.

Her new fiefdom is, after all, so populated by millionaires in their exclusive enclaves that it is the second richest city in the world’s richest nation.

Considering the city’s wealth, it smacks of callous and uncaring hypocrisy.

As one local resident says: ‘Are they really being progressive to that poor guy in the street with a needle in his arm who is going to die tomorrow?’

Be seeing you

The beautiful city by the bay, where Tony Bennett famously left his heart and which poses as a beacon of progressiveness, has more billionaires per capita than any other on the planet. Not long ago, a seven-bedroom home here recently sold for $38 million (£29 million), while at the Michelin-starred Saison restaurant, the ¿kitchen menu¿ starts at $298 a head and reservations require a $148 deposit


Posted in Uncategorized | Tagged: , , , , | Leave a Comment »

Coronavirus Update – PaulCraigRoberts.org

Posted by M. C. on February 3, 2020

DARPA, for instance, has been developing a series of unsettling research projects that ranges from microchips that can create and delete memories from the human brain to voting machine software that is rife with problems.

Also left out of the media narrative have been the direct ties of both the USAMRIID and DARPA-partnered Duke University to the city of Wuhan, including its Institute of Medical Virology.

https://www.paulcraigroberts.org/2020/02/02/coronavirus-update/

Paul Craig Roberts

Using more recent data from China of the coronavirus’ infection and death rates than the Indian scientists had, “Moon of Alabama” concludes that the “pandemic” has reached its peak and will be over with in a month.

https://www.moonofalabama.org/2020/02/coronaupdate.html

If so, then Jon Rappoport was correct in the beginning that coronavirus was just another big scare hype.

https://www.paulcraigroberts.org/2020/01/28/coronavirus-a-real-threat-or-another-scare/

Let’s hope that this is the case and that the coronavirus is a far less threat than ordinary flu. Nevertheless, such a happy outcome still leaves us with a lot of puzzling questions.  Here are a few of them:

  1. Why such an enormous effort by the Chinese government using draconian quarantine measures affecting millions of people and multi-country halts of travel to and from China over a threat far less serious than ordinary flu?
  2. Why is there a rush to develop a vaccine?
  3. Why the expert predictions of a worldwide pandemic?
  4. Why did the virus originate in a Chinese city known to have labs for the study of dangerous viruses?
  5. Why do the scare viruses originate in China—SARS, swine flu, bird flue, coronavirus?
  6. Why did the team of scientists in India find elements of HIV in the coronavirus genome that is believed to raise the infectious potential, a finding, if correct, implies the engineering of a bioterror weapon?

The scientists might be wrong, but they are not presenting a conspiracy theory.  They published their paper provisionally in order to get input from other scientists.  I have no idea whether their findings will be validated, and whatever we are told, we might never know.  If the virus proves to be bioengineered, the Chinese government will know whether something they did escaped.  If they are not responsible for the virus, they will perceive an attack on them by the US.  This type of information would confirm Chinese suspicions:

“Research conducted by the Pentagon, and DARPA specifically, has continually raised concerns, not just in the field of bioweapons and biotechnology, but also in the fields of nanotechnology, robotics and several others. DARPA, for instance, has been developing a series of unsettling research projects that ranges from microchips that can create and delete memories from the human brain to voting machine software that is rife with problems.

“Now, as fear regarding the current coronavirus outbreak begins to peak, companies with direct ties to DARPA have been tasked with developing its vaccine, the long-term human and environmental impacts of which are unknown and will remain unknown by the time the vaccine is expected to go to market in a few weeks time.

“Furthermore, DARPA and the Pentagon’s past history with bioweapons and their more recent experiments on genetic alteration and extinction technologies as well as bats and coronaviruses in proximity to China have been largely left out of the narrative, despite the information being publicly available. Also left out of the media narrative have been the direct ties of both the USAMRIID and DARPA-partnered Duke University to the city of Wuhan, including its Institute of Medical Virology.

“Though much about the origins of the coronavirus outbreak remains unknown, the U.S. military’s ties to the aforementioned research studies and research institutions are worth detailing as such research — while justified in the name of “national security” — has the frightening potential to result in unintended, yet world-altering consequences. The lack of transparency about this research, such as DARPA’s decision to classify its controversial genetic extinction research and the technology’s use as a weapon of war, compounds these concerns. While it is important to avoid reckless speculation as much as possible, it is the opinion of this author that the information in this report is in the public interest and that readers should use this information to reach their own conclusions about the topics discussed herein.”

https://www.blacklistednews.com/article/76139/bats-gene-editing-and-bioweapons-recent-darpa-experiments-raise-concerns-amid-coronavirus.html

If the Indian scientists’ findings are correct, we should expect them to be shouted down by government supported scientists.  To save their careers, they would have to acknowledge a mistake in their research.  If the virus were a US manufactured one, China would have the same incentive to coverup the fact as Washington, because otherwise the consequence would be war, for which China is not ready.

There are other concerns.  For example, concurrent with the announcement of the new virus there were accusations that the Chinese virus lab was responsible for the pandemic threat and might even have released it purposely on its own population. Moon of Alabama is correct to call this a conspiracy theory.  It is a conspiracy theory to discredit the Chinese government with the Chinese population and the rest of the world.  The Chinese government has no interest in harming the Chinese economy and discrediting itself with a population that it is trying to rule without a harsh hand, but Washington has an interest in ruining the Chinese.

I think it is a good thing that the question whether coronavirus is an engineered virus came up. There are a number of secret high security labs around the world doing scary things.  As Whitney Webb writes, “The lack of transparency about this research, such as DARPA’s decision to classify its controversial genetic extinction research and the technology’s use as a weapon of war, compounds these concerns.”  There is a treaty—or was as Washington might have pulled out of it like it has the arms control agreements with the Russians—that supposedly prevents countries from making bioweapons.  However, whether they are making the weapons or not, they are doing research that could quickly be weaponized.

Perhaps it would be a good thing if there were a worldwide public discussion whether the benefit of the research is greater than the risk of a deadly pandemic.  The lack of transparency makes mischief possible.  Remember the anthrax letters in the wake of 9/11 that turned out to contain a version of anthrax available only in a US government lab.  To cover this up, the letters were blamed on a dead man who had no motive to send the letters and no access to the anthrax.  Something as dangerous as bioengineered pathogens require plenty of transparency.

There is no reason scientists should be permitted to investigate whatever they want.  Think for a minute, what is the good of nuclear weapons?  Perhaps if Earth were invaded by hightech Aliens, thermonuclear weapons could be a defense.  Perhaps if an astroid is on collision course with Earth, nuclear missiles could shatter it into small pieces that would burn up in the atmosphere or into smaller pieces that would do less damage.  What else are nuclear weapons good for but to bring us Armageddon?

A lot of thought is needed also about robotics and artificial intelligence.  Robots such as those that can withstand deep underwater pressures and radiation are useful.  But robots that displace people can leave humans unemployed and without purpose.  And do we really want machines as smart or smarter than humans or weaponized?

The challenges of these technologies can be very interesting to scientists, but the unintended and ignored consequences can be horrific.

An obvious question is:  If people with white skin cannot use certain words or long-established expressions, cannot read, study, or teach certain subjects that some believe are offensive, and cannot organize or segregate themselves as others are permitted to do, why can scientists and governments study and manufacture things that could terminate life itself?  This makes no sense.  If we do not begin to make better sense soon, conspiracy theories are going to become very real.

We cannot rely on the ethics and morality of governments.  They have neither.  Consider the US and its European vassals.  For 20 years they have bombed, invaded, murdered, and ravaged seven countries, destroying them in whole or part, all on the basis of transparent lies.  And nothing is done about it. Indeed, the murderous process continues.

Based on these transparent lies, President George W. Bush violated the US Constitution and held indefinitely American citizens on suspicion alone, and President Obama violated due process by executing US citizens on suspicion alone.

Neither were impeached.  Congress, the judiciary, and the public accepted this shredding of the US Constitution and stepped into a police state.  When there is no honest media to protect the people, government transparency becomes even more critical.

Since 2009, the US government has overthrown governments in Honduras, Ukraine, Bolivia, Brazil, Argentina, reversed the reform process in Ecuador, temporarily overthrew Chevez in Venezuela and continues to try to overthrow his successor Maduro. Cuba, North Korea, Syria, Iran, Russia, and China remain on Washington’s list of countries to be overthrown.

This extraordinary arrogance is easily capable of using a false flag engineered pathogen to produce termoil within a country that collapses a government.  For this reason, the transparency of research is of the upmost importance.

Be seeing you

Flu Prevention Amid Coronavirus Scare (1-30-20) - One News ...


Posted in Uncategorized | Tagged: , , , , | Leave a Comment »

Can Bernie and Tulsi Survive Hillary’s ‘Urge’ to Save the DNC? — Strategic Culture

Posted by M. C. on February 3, 2020

This is Bernie’s last kick at the can. He’s already gotten the gold watch from the DNC in 2016, living the high life only a high member of the Politburo can.

Gabbard has burned all the bridges within the DNC she can, almost gleefully. That makes her a person of integrity, of authenticity, in a U.S. political wasteland of charlatans, reality show hucksters and outright thieves.

The quicker she climbs out of the basement in Pelosi’s House, the better off she’ll be.

https://www.strategic-culture.org/news/2020/02/01/can-bernie-and-tulsi-survive-hillarys-urge-to-save-the-dnc/

Tom Luongo

For months now I’ve been convinced that Hillary Clinton will be entering the fray that is the Democratic Party primary season. The affair to date has been a nothing short of high comedy.

Recent events have me more convinced than ever that she will be returning, like some zombie whose head we forgot to cut off, to haunt voters one more time this fall.

After the beginning of an obvious (and planned) PR campaign last week with the release of a big campaign ad documentary on Netflix and a big splash in the Hollywood Reporter Hillary finally stopped being coy. And she announced this week that she now ‘has the urge’ to run again against Donald Trump.

Save us, please, from Hillary’s urges…. Shudder.

And she did so making sure that everyone knew what she thought of the real front-runner for the nomination, Bernie Sanders.

As various anointed ones have dropped out of the race – Kamala Harris, Cory Booker, Robert O’Rourke – others have faltered despite huge ad spends while the media and pollsters do their level best to convince us all that Joe Biden’s a serious candidate to take on Donald Trump this fall.

In fact, the only reason Biden is still in the race is to make the impeachment theater going on right now seem relevant and cogent. But, like Biden himself, it is neither.

Then again neither is Hillary, but never underestimate this woman’s narcissistic solipsism.

If you look back on the race to date it’s clear that most of the people running are there to try and distract voters away from the two candidates that resonate most with voters, Bernie Sanders and Tulsi Gabbard.

Yes, Gabbard is polling low but if you look at poll numbers versus money spent and/or raised to this point, she’s clearly got cache and the ability to build a real following. And as the field shrinks those distractions become irrelevant. Her poll numbers are rising the more the field winnows.

Neither of them is acceptable in any way to the DNC. They are outsiders within their party. I’m no fan of Bernie Sanders. In fact, I think he’s a terrible candidate — because, you know, commie! — but that’s not the point of this article.

Bernie is surging in the early states and panic is setting in with the DNC. And they must have a plan to stop him from running away with the nomination otherwise we could have two outsiders headlining this fall’s reality show.

And that plan starts with the impeachment and potential removal of Donald Trump.

The impeachment is a distraction for Trump but it is a real problem for the Senators running for the Democratic nomination. They have to spend all day listening to Adam Schiff and Jerry Nadler lie while they could be out campaigning and raising money.

This hurts Bernie the most because Bernie is the one who will get zero help from the DNC’s big donors. None of them are behind him and with good reason. He’s hostile to most of them (and most of us as well, but that’s a different article).

Of the people running for President as Democrats the only person less acceptable to Wall St. than Elizabeth Warren is Bernie Sanders. Warren’s entire campaign has been designed to push Bernie farther left by out-lefting him at every turn. Bernie says 70% top marginal tax rate, Warren says 77%. Bernie wants debt restructuring? Warren says forgive all student loan debt.

Her job is to make Bernie as unacceptable to mainstream U.S. voters as possible. Unfortunately, that makes Bernie more and more acceptable to a lot of people voting in the Democratic primaries. And this Catch-22 is beginning to show up in the polls for Iowa and New Hampshire.

Then there’s the serious money behind Pete Buttigieg trying to create slightly gayer version of Barack Obama. Again, he’s just another distraction to suck support away from Sanders and keep the field relatively close and the odds of an uncommitted primary season high.

Because the goal is to get to a brokered convention this summer. So, the impeachment was slowed down to hurt Sanders, Warren and Amy Klobuchar and help give Biden the bump he needs to get some momentum coming into Iowa.

It’s not working.

But I also don’t think it’s going to matter. If you keep watching the headlines the attack dogs are out in full to discredit and hurt Sanders. They know he’s a real force to be reckoned with. And worse, his attack dog, Gabbard, has been muzzled by keeping her off the debate stage so she can’t take anyone else out, like she roasted that pig Kamala Harris last summer.

But I truly feel the DNC is looking to steal the nomination again from Sanders. And the impeachment of Trump continues to somehow, against all odds, get worse for him, even though his party is supposed to be in charge of the proceedings.

I told everyone back in September when Nancy Pelosi announced she was going through with the impeachment process that this was all about getting rid of Trump. But it was in October when Hillary went after Tulsi Gabbard that  Gabbard’s response was beyond epic and I wrote about it then.

Gabbard throws down the gauntlet here outing Hillary as the mastermind behind the DNC strategy of allowing the current crop of future losers to fall all over themselves to alienate as many centrist voters as possible.

This paves the way for Hillary to swoop in on her broom, pointed hat in hand, and declare herself the savior of the Democratic Party’s chances to defeat Donald Trump next November.

So, Hillary’s running, the DNC is trying to stop Bernie and Tulsi Gabbard is still an also-ran in New Hampshire and Iowa, polling between 5% and 7%. So what?

Well, I feel at this point it’s been game-planned by Gabbard and Sanders that they know what’s coming. I felt the endorsement from Joe Rogan of Sanders was timed to distract from Hillary’s attack on Bernie in that Hollywood Reporter piece.

Rogan is far more influential than the dead tree media Hillary’s publicist works with. And her attack dogs were out in full to attack Rogan and smear Sanders with their typical guilt-by-association nonsense.

I don’t tweet much folks, but this one gets to the truth of what’s going on in the murk and slime of Democratic Party politics.

Sanders and Gabbard know the DNC is out to destroy him. And the question then becomes what’s next?

What do they do to combat this? Gabbard is not running for re-election in Hawaii. She says she’s committed to running for President. I don’t think she’s getting the nomination and, frankly, I don’t think she is either.

She just filed a defamation of character lawsuit against Hillary for the smears Hillary threw around I linked to above. She puts financial pressure on Hillary knowing that the Clintons couldn’t drum up support and dollars last year during their expensive speaking tour no one went to.

Gabbard denies any kind of third party run, getting the Ron Paul treatment from the media. But, she’s a very acceptable person to a lot of disaffected Trump voters like myself. She speaks to them and can help carry Bernie as his running mate if he somehow makes it through the convention to be the Democratic nominee.

So, yes, Gabbard isn’t running for re-election because she’s running as Sanders’ Vice-Presidential candidate.

And it may not be for the Democratic party in the end. That’s the part you have to factor in here.

Game-planning this out, these two are running a real insurgency within the DNC to either get the nomination or split off and run as Independents. This is Bernie’s last kick at the can. He’s already gotten the gold watch from the DNC in 2016, living the high life only a high member of the Politburo can.

Gabbard has burned all the bridges within the DNC she can, almost gleefully. That makes her a person of integrity, of authenticity, in a U.S. political wasteland of charlatans, reality show hucksters and outright thieves.

The quicker she climbs out of the basement in Pelosi’s House, the better off she’ll be.

I don’t put it past either of these people to think that preventing Hillary from regaining control of the Democrats and spoiling her return is the best outcome for America, even if it re-elects Donald Trump.

But, if Trump is removed to make way for Hillary, then the Race to 270 electoral votes becomes a non-binary affair.

© 2010 – 2020 | Strategic Culture Foundation | Republishing is welcomed with reference to Strategic Culture online journal www.strategic-culture.org.

Be seeing you


Posted in Uncategorized | Tagged: , , , , | Leave a Comment »

What to watch for in governor’s budget proposal – Erie Times E-Edition Article

Posted by M. C. on February 2, 2020

http://erietimes.pa.newsmemory.com/?publink=24e52dd54

What to watch for in the (PA) governor’s budget proposal

“It is laboring under an estimated $67 billion debt in its two large public sector pension systems”

The Tom Ridge legacy.

“Persistent cost increases for health care, prisons and pensions can be expected to absorb much of the state’s natural growth in tax revenues.”

We have had a national health department since 1939. We might as well have called it the war on health as cost wise it has had the same result as the wars on drugs, poverty and terrorism. We should expect better after 80 years.

We have the highest per capita prison population on the planet. Manly due to the failed war on drugs filling prisons with non-dangerous offenders. Illegal drug trade has turned Mexico into a disaster.

Education

“Wolf is expected to continue his five-year push to give more money to public schools amid a lawsuit accusing the state of harboring deep inequities in how it funds the poorest public schools.”

It is no secret a major education expense is the skyrocketing administration load which surpasses enrollment rates.

It is time to trash all the “Therian studies and acceptance” programs, safe rooms and the plethora of administrators and get back to being grownups.

The state runs these programs, not grownups, and that is why the hole keeps being dug deeper. The solution will never come from the “state”.

Be seeing you

facebook_1574076533302.jpg


Posted in Uncategorized | Tagged: , , , , , , | Leave a Comment »